

 Cinema Portal
 Election Portal
 Share Dhani Portal
 Unicode Page
 English Edition
 Share Training
 PREMIUM
 सुन-चाँदीको भाउ
 विदेशी विनिमयदर
 मिति रुपान्तरण
 पेट्रोलको भाउ
 तरकारी/फलफूल भाउ
 आर्थिक राशिफल
 आजको मौसम
 AQI Page



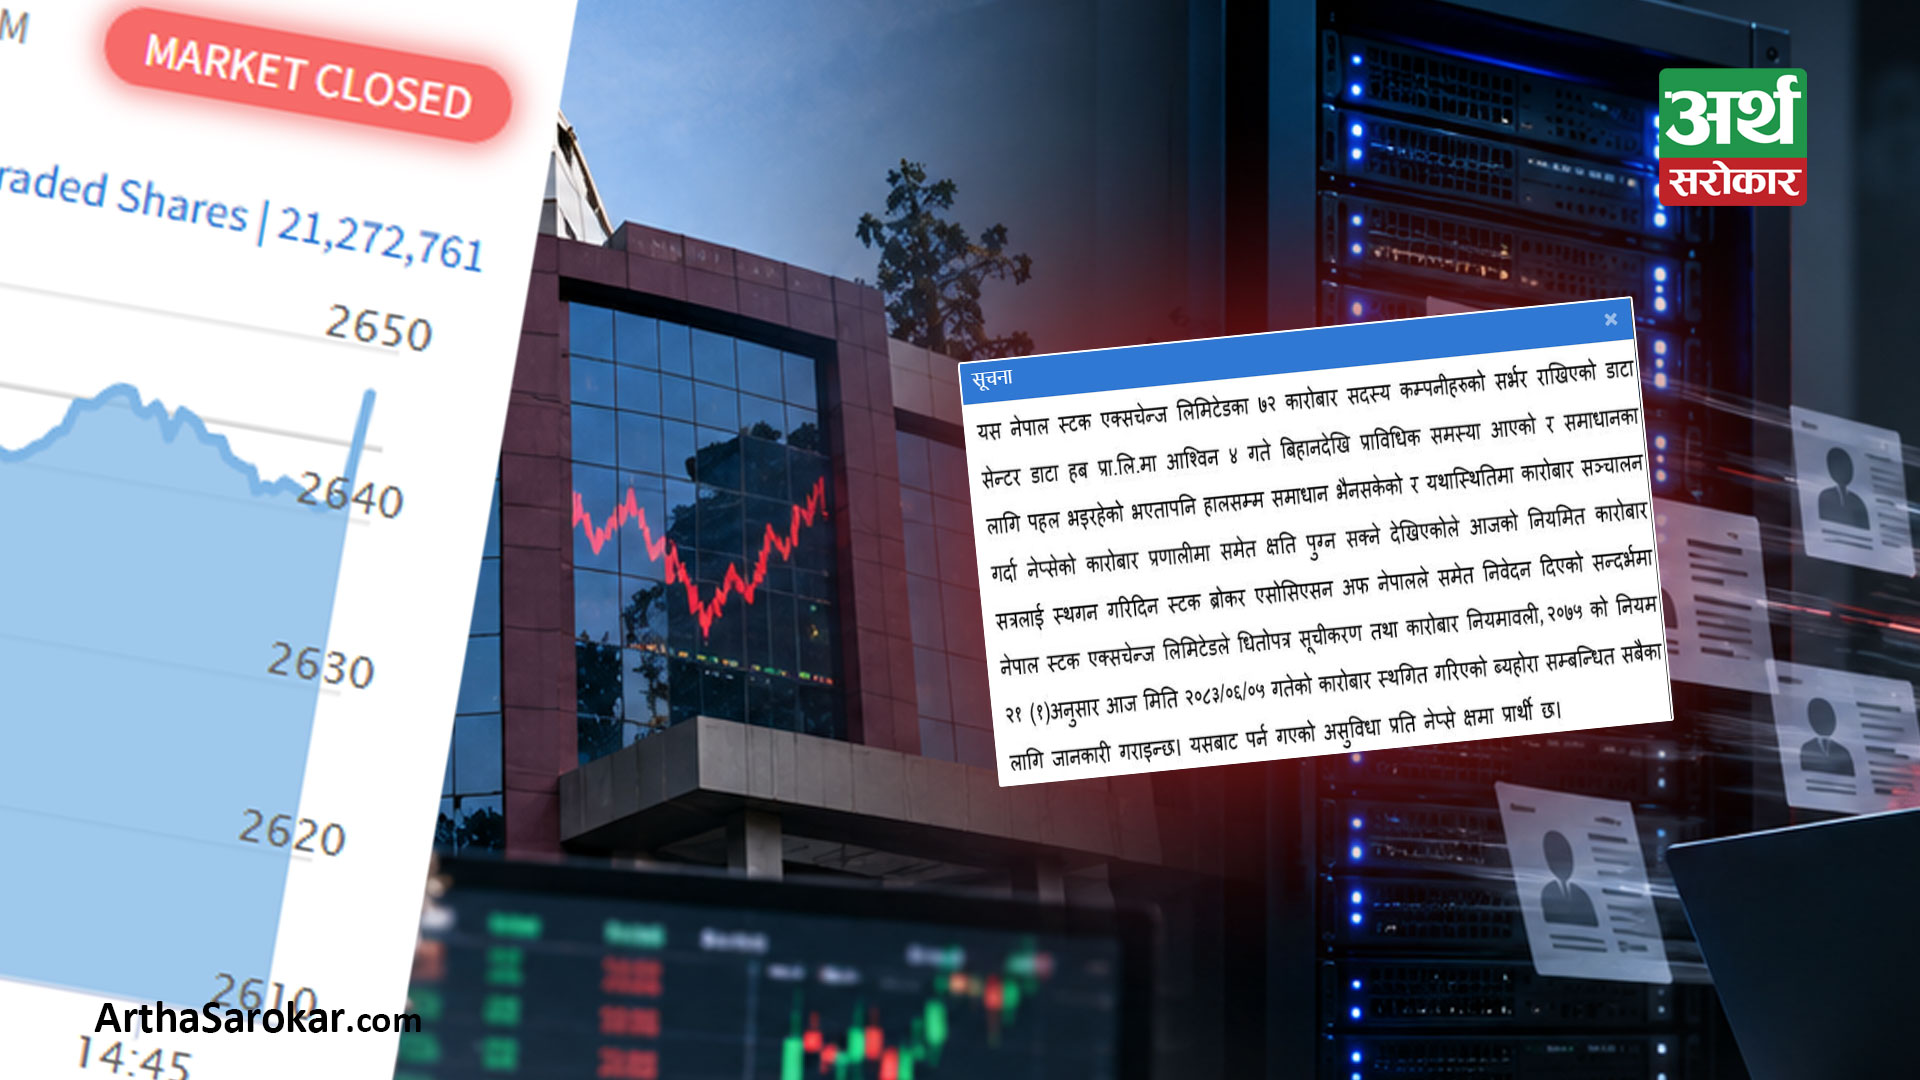
Kathmandu. Yes, we had said in the year 2080 by showing evidence that Nepse’s small system is at great risk, it can be hacked at any time. At any time, the transaction details related to the future of millions of investors can reach the hacker. The details of who bought or sold which shares can be found on the dark web, those data can be traded by paying money in the market. And due to the negligence and mischief of a careless company named Waiko and the negligence of the owner of the data hub who runs the same team, the entire stock market system of Nepal can be attacked. We did not say this fact without reason, we showed the fact that Nepse’s IT audit report said, showing the flaws pointed out by the report prepared by the Securities Board itself but kept secret till now. Nepse’s data can reach the hacker at any time. And in the end, whatever happened is what we wanted to happen. The details of millions of investors reached the reach of the hackers. The hackers were targeted by the crooked monkeys sitting on the chair over the investors’ data. And now, no matter how much they try to cover it, it is seen naked – all the details of the investors have reached the reach of the hacker. And as at any time, more accidents can happen.
The Securities Board of India (SEBI) report said that “there is a risk of misuse of details”
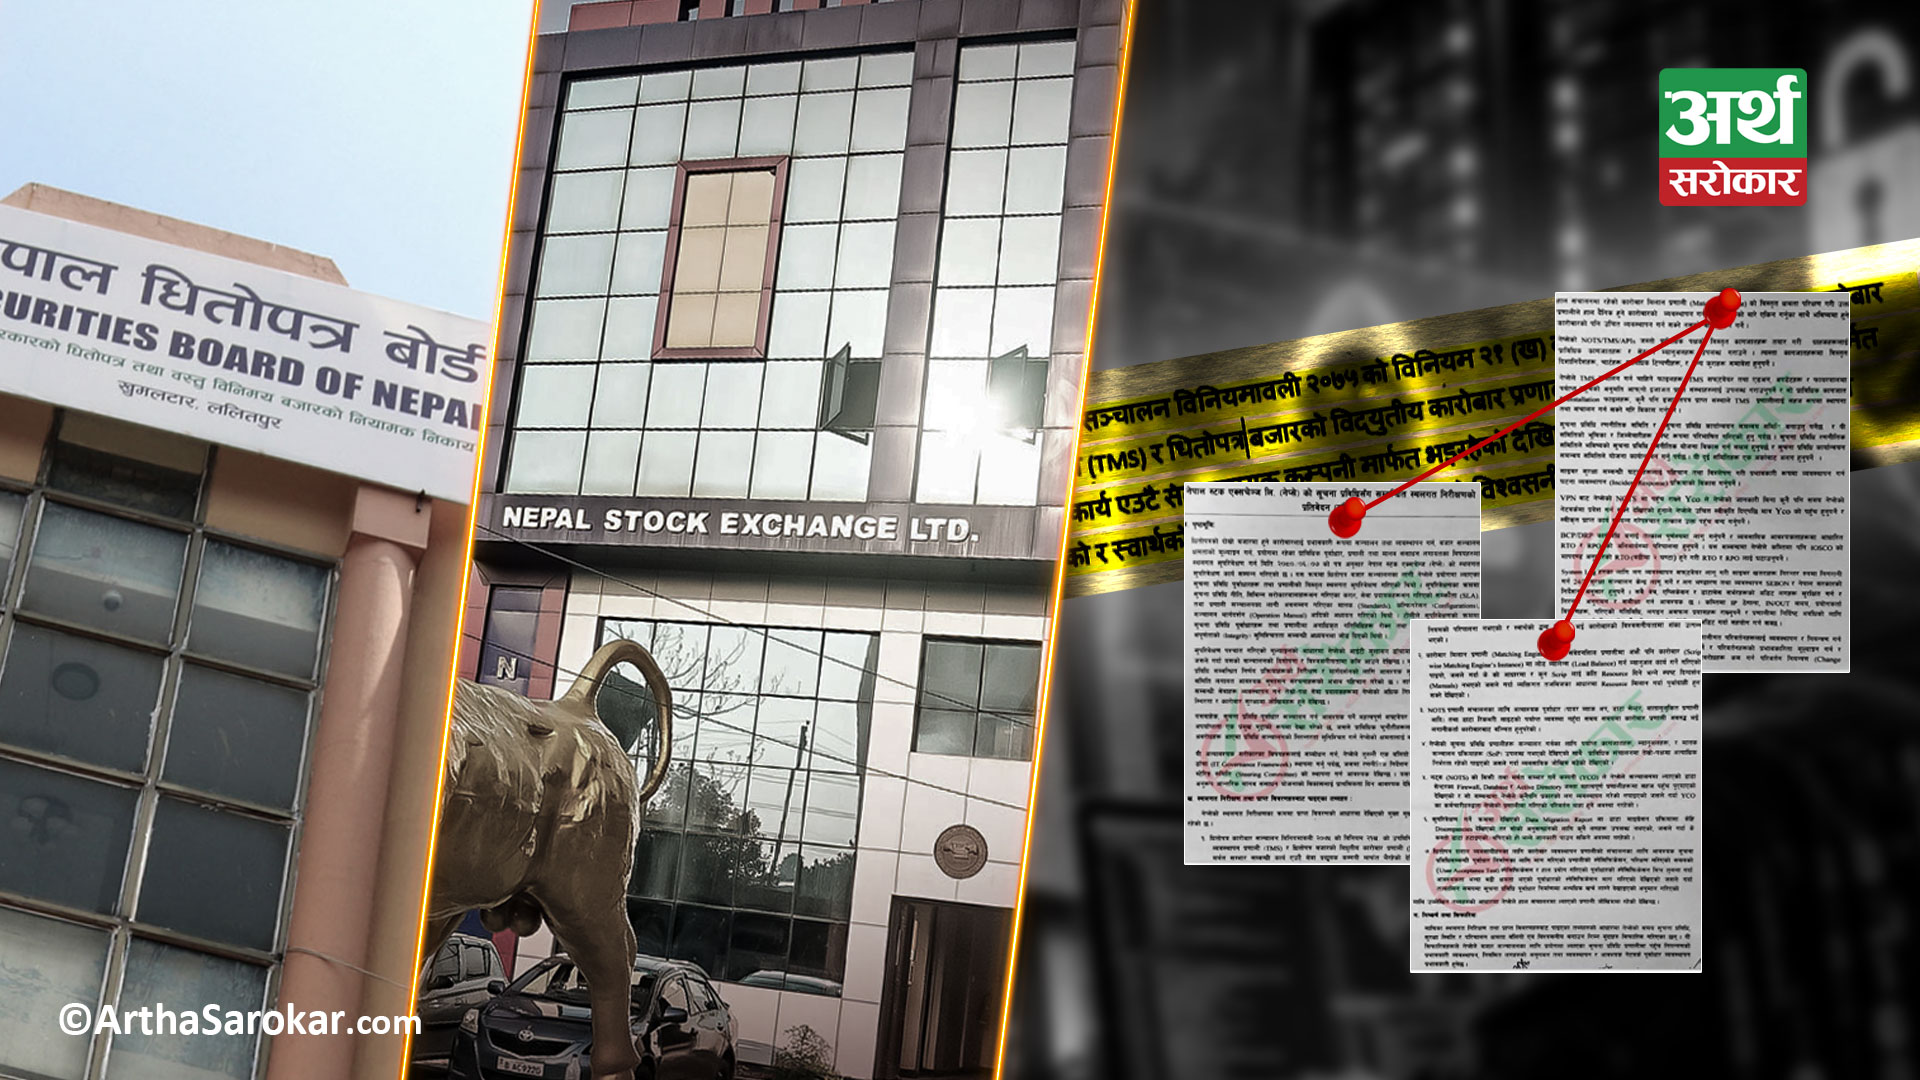
The Securities Board of Nepal (SEBON) had formed an investigation committee to conduct an IT audit of Nepse after complaints that Waico buys and sells the details of the share investors, the employees there sell the details of who bought which shares.
The Securities Board of Nepal (SEBON) formed a team of directors Rewat Shrestha and Sanu Khadka and assistant directors Yamnath Aryal and Rabindra Dev Bhatta under the coordination of the board’s information technology expert Saroj Lamichhane, and the report submitted to the board on the information technology governance of the market. The board itself fired at NEPSE after knowing that unauthorized people would have easy access to the system. The Securities Board of Nepal did not even make this report public as it was found that there was a danger that the stock market would be run by someone. The board has still kept this report secret. But 2 years ago, we made this report public and said that Nepse’s system can be hacked at any time. Let’s not be so mischievous in the setting, let’s not make such a crude joke on the data of investors. But who will touch Waiko? The political connection of the data hub opened under the guise of Waiko was so strong, who would run it? After that, some CEOs changed in NEPSE, but no one could speak on this issue. Perhaps, it was the same ‘Ba’ who appointed them and made a company that made inferior software like Waiko.
During the study, Nepse’s system was found to be so efficient that it was as if Nepse is remembering its online system like a video game. Nepse’s online system was found to be so insecure that suppose some people in Nepse can do anything at any time.
Let’s understand it more technically. In fact, Waico was given the responsibility of selling and maintaining the trading system of the Nepali stock market, which is called Nuts for short. It had only the nuts that it had to look at. But the board itself found that Waico had access to the entire system of Nepse. The study of the board itself showed that if it wanted, it could enter the TMS of the brokers, not allow any script to run, put a buy order in some of them, and not show the buy order in some. The report said that Waico even had access to the data center operated by Nepse, easy access to important systems such as Nepse’s database and active directory. This means that if someone placed a buy order in one script, Waico could manipulate the data without showing it, if someone placed a sell order, Waico could even distort the data to show that there was no cell in that script. In more simple terms, Waico could either increase the increase of one script, or if it wanted, it could reduce the decrease. It was not a big deal that those who did so much could hack the system. Even when an ordinary employee got angry, there was a risk that the system would be hacked. And in the end, it happened. One day, the system was attacked, so that the share trading had to be stopped. Whether this attack was done by the employees of the Data Hub, the employees of Waiko, or by an external hacker, it is not clear from the investigation, but those who make the system weak or do not improve it even after knowing that it is a weak system are the factors in this case. They need to be brought under the purview of action.
IS audit also showed ‘Kafiyat’!
Not only the Securities Board of Nepal, but the ‘Information System Audit’ (IS Audit) conducted by Nepse to examine all the IT-related systems, including the trading system, had revealed that Nepse’s trading system was unsafe. This report was also hidden by Nepse and the financial concern was broken. Even now, NEPSE has not dared to make the report public.
The trading system of Nepse was built by Waiko. In the IS audit report of Nepse, obtained from a confidential source, it was said that the entire system of Nepse’s trading system was under the supervision of Waico, and Waico could make any kind of sensitive changes and Nepse could not even track it. The report had also revealed that giving Waico full access to the system could lead to any accident. In the report, this security weakness of Nepse was described as the most ‘critical’. In the report, it was also recommended that an approval system should be put in place as the entire system is within the reach of the vendor i. e. Waiko, it can pose any kind of risk.
The report also revealed that any kind of ‘attack’ can occur in Y’s system at any time. The report had presented the intention that if the IP policies were not defined in Nepse’s system, there could be unauthorized access to Nepse’s network equipment and servers by taking advantage of the weakness in the system and any hacker could easily hack Nepse’s system.
The report said that even with the use of VPN, the vendor had full access to the system and since the details or action logs of the same were not with Nepse, any kind of unauthorized access to Nepse’s system could take place in Waiko’s settings, all the data in the system could be leaked, the company’s sensitive data and even the details in the transaction system could be leaked. But the audit showed such flaws as a general bug. We shouted and said that any day there could be an accident, all the systems of Sara could reach the hacker. But at that time, no one took this seriously. Because they were enjoying commissions, transactions and so on. But finally the data of Nepse has reached the reach of the hackers, we do not know how many more accidents will happen, we do not know how much of the data that has reached the reach of the hacker will be misused.
Waiko’s mischief and Nepse’s helplessness hacked the system!
The Securities Board had said that there is a problem with Nepse’s system, it can be hacked at any time, it can be improved. But no one was ready to improve. The IS audit report of Nepse itself had said that unauthorized people have access to the system, do not do this, improve. But neither Nepse nor Waiko. No one had time to improve. And what happened, what should not have happened, happened. Nepse’s data was completely in the possession of hackers. Just as the floods of Rasuwa swept everything away, the data of all the investors reached the hackers in one click.
Far from correcting their weaknesses, Data Hub and Waico were embarrassed and asked to stop today’s business. After all the data reached the reach of the hackers, there was nothing that could be done by shutting down the business for a day. But by showing a formal series of correspondence and statements, Y Hub and Data Hub are still hiding the weakness of their weak system.
This is not the first time that Nepse’s system has been hacked. I pray that it does not happen, but it is not the last time. Because saying that the same Y, the same data hub will improve Nepse’s system and saying that the same old corrupt leaders will develop the country is the same.
In recent times, the government has become ruthless against those who are involved in irregularities in the NSC, irregularities in the CAN. Even now, if the system of Nepal’s stock market is not protected from the virus with the setting of the name of Y, then it will not be surprising if one day the market crashes with a hacker. Because those who set up have nothing to worry about except the setting. Those who do not care about the loopholes that are openly seen in the system with their name attached, then they do not have to worry about the country, the stock market. Government! Again we are saying be ruthless about those who left the way for hackers to enter the system, who have been making fun of the billions of transactions of stock investors for years. And conduct an impartial investigation, who has sold the data where. Because, those who make money by selling public data cannot love the country. (Video)
https://www. youtube. com/watch? v=HqWc6P5ZyJc&t

प्रतिक्रिया दिनुहोस्